
A backup is useful only if the business can restore data when something goes wrong. Many small companies believe they are protected because files are synchronized to the cloud or copied to an external drive. The problem is that synchronization, storage, and backup are not the same thing. If a deleted or encrypted file is immediately synchronized across every device, the business may discover that its supposed backup contains the same damaged version.
A working backup strategy starts with understanding which data keeps the company operating and how quickly that data must return after an incident. The same logic applies to any digital service that depends on stored information, whether the business manages invoices, customer records, product files, or an online environment connected with jili fortune garuda 500: availability matters only when the system can recover from failure without losing the information required to continue operations.
Identify the Data That Must Be Recovered First
The first step is not choosing backup software. It is deciding what must be protected.
A small business should list its critical data: accounting records, contracts, customer databases, shared documents, project files, employee records, website files, product images, and internal procedures. Some information may be replaceable, while other files may represent years of work.
The company should then rank data by business impact. Losing a marketing draft may be inconvenient. Losing payroll records or active customer contracts may stop operations.
This priority list determines how frequently each category should be backed up and how quickly it must be restored.
Separate Backup From File Synchronization
Cloud synchronization is convenient because employees can access the same files from several devices. It should not automatically be treated as a complete backup system.
If an employee deletes a folder, the deletion may synchronize to every connected device. The same can happen when ransomware encrypts files or a compromised account modifies them.
A real backup keeps independent copies from earlier points in time. The business should be able to restore yesterday’s version even if today’s version is corrupted.
Version history can help, but companies should understand how long previous versions are retained and whether an attacker with administrator access could delete them.
Use the 3-2-1 Backup Principle
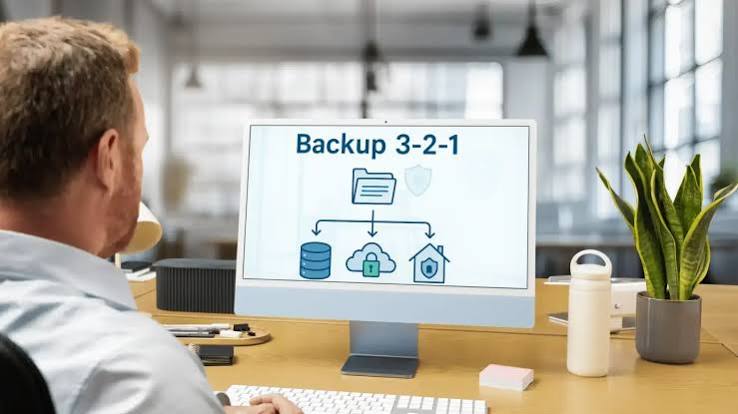
A practical foundation is the 3-2-1 approach: keep three copies of important data, use two different storage types, and maintain at least one copy away from the primary environment.
The working file counts as the first copy. A local backup may be the second. An off-site or isolated backup becomes the third.
The purpose is to prevent one incident from destroying every copy at once. A hardware failure can affect the office computer and an attached drive. Ransomware can reach network storage. Theft or fire can remove equipment from one location.
Keeping copies in different environments reduces the chance of a single event causing total data loss.
Protect Backups From Ransomware
A backup connected permanently to the same systems as production data can become another ransomware target.
Attackers often search for backup folders, network drives, and administrator tools because destroying recovery options increases pressure on the victim.
At least one backup should therefore be difficult to modify from ordinary employee accounts. This may involve offline storage, restricted credentials, immutable storage, or a separate backup account.
Backup administrator credentials should not be identical to normal workplace credentials. If one employee account is compromised, the attacker should not automatically gain permission to delete recovery copies.
Decide How Often Backups Should Run
Backup frequency should reflect how much recent work the business can afford to lose.
If accounting data changes throughout the day, a weekly backup may be insufficient. Losing six days of invoices and payments could require extensive reconstruction.
A business should define a recovery point objective: the maximum acceptable period of lost data. If the company can tolerate losing only four hours of work, backups need to run at least that often.
Different systems can have different schedules. Customer databases may require frequent copies, while archived design files may need less frequent protection.
Define How Fast Recovery Must Happen
Businesses also need a recovery time objective, which defines how long a system can remain unavailable.
Restoring a few documents may take minutes. Rebuilding a server, database, or full file environment may take much longer.
The company should estimate how downtime affects operations. If employees cannot issue invoices without one folder, that folder deserves a faster recovery process than files that are rarely used.
This helps determine where backup resources should be concentrated instead of applying the same recovery level to every file.
Encrypt Backups and Control Access
Backups contain the same sensitive information as the original systems. Sometimes they contain even more because they include historical versions that have already been removed from active storage.
Backup data should therefore be encrypted and access should be limited.
Only employees or service providers responsible for recovery should have administrative permissions. Activity logs should be available where possible, particularly for deletion, configuration changes, and login attempts.
The company should also document who controls recovery credentials so access does not depend on one employee being available.
Test Restores Instead of Trusting Backup Reports
A backup system can report success while still producing files that cannot be restored correctly.
This is why restore testing is essential. The business should periodically select files or systems and recover them into a test location.
The test should answer practical questions: Are the files complete? Can they be opened? Are permissions preserved? How long does recovery take? Does the team know the procedure?
A backup that has never been tested is only an assumption.
Document the Recovery Process
During an incident, employees should not have to invent the recovery process under pressure.
A short recovery document should identify backup locations, responsible people, account recovery steps, restore priorities, and external contacts.
The instructions should also explain what happens if the main administrator account is unavailable or compromised.
This documentation reduces dependency on individual memory and helps the company respond faster when normal systems are inaccessible.
Backups Must Be Designed for Failure
The purpose of a backup system is not to create copies. It is to make recovery possible after deletion, ransomware, hardware failure, account compromise, or human error.
A reliable setup combines multiple copies, separate storage, limited access, frequent backups, defined recovery targets, and regular restore tests.
For a small business, the most important question is simple: if the main files disappeared today, could the company restore the right version without depending on the damaged system? If the answer is uncertain, the backup strategy still needs work.
